A technical breakdown of the largest AI agent supply chain attack to date and why "just install a skill" is the new "just download this executable"
TL;DR: Security researchers discovered 341 malicious skills in ClawHub, the extension marketplace for OpenClaw agents. The attack, dubbed ClawHavoc, deployed credential-stealing malware on both macOS and Windows, exfiltrated API keys, cryptocurrency wallets, and SSH credentials. Snyk's follow-up audit found that 36% of the entire AI skills ecosystem contains security flaws. The root cause is architectural: agent marketplaces combine the worst properties of browser extension stores and npm registries, with none of the security infrastructure that took those ecosystems decades to build.
The Attack
On February 2, 2026, Koi Security published findings from a security audit of ClawHub, the primary extension marketplace for OpenClaw, a popular self-hosted AI assistant. The researchers examined 2,857 skills available on the platform.
They found 341 malicious ones.
The attack campaign, which researchers named ClawHavoc, was sophisticated in its simplicity. The malicious skills masqueraded as legitimate applications: Solana wallet trackers, Polymarket trading bots, YouTube summarization tools, Google Workspace integrations. Their documentation looked professional. Some had fake download counts and reviews.
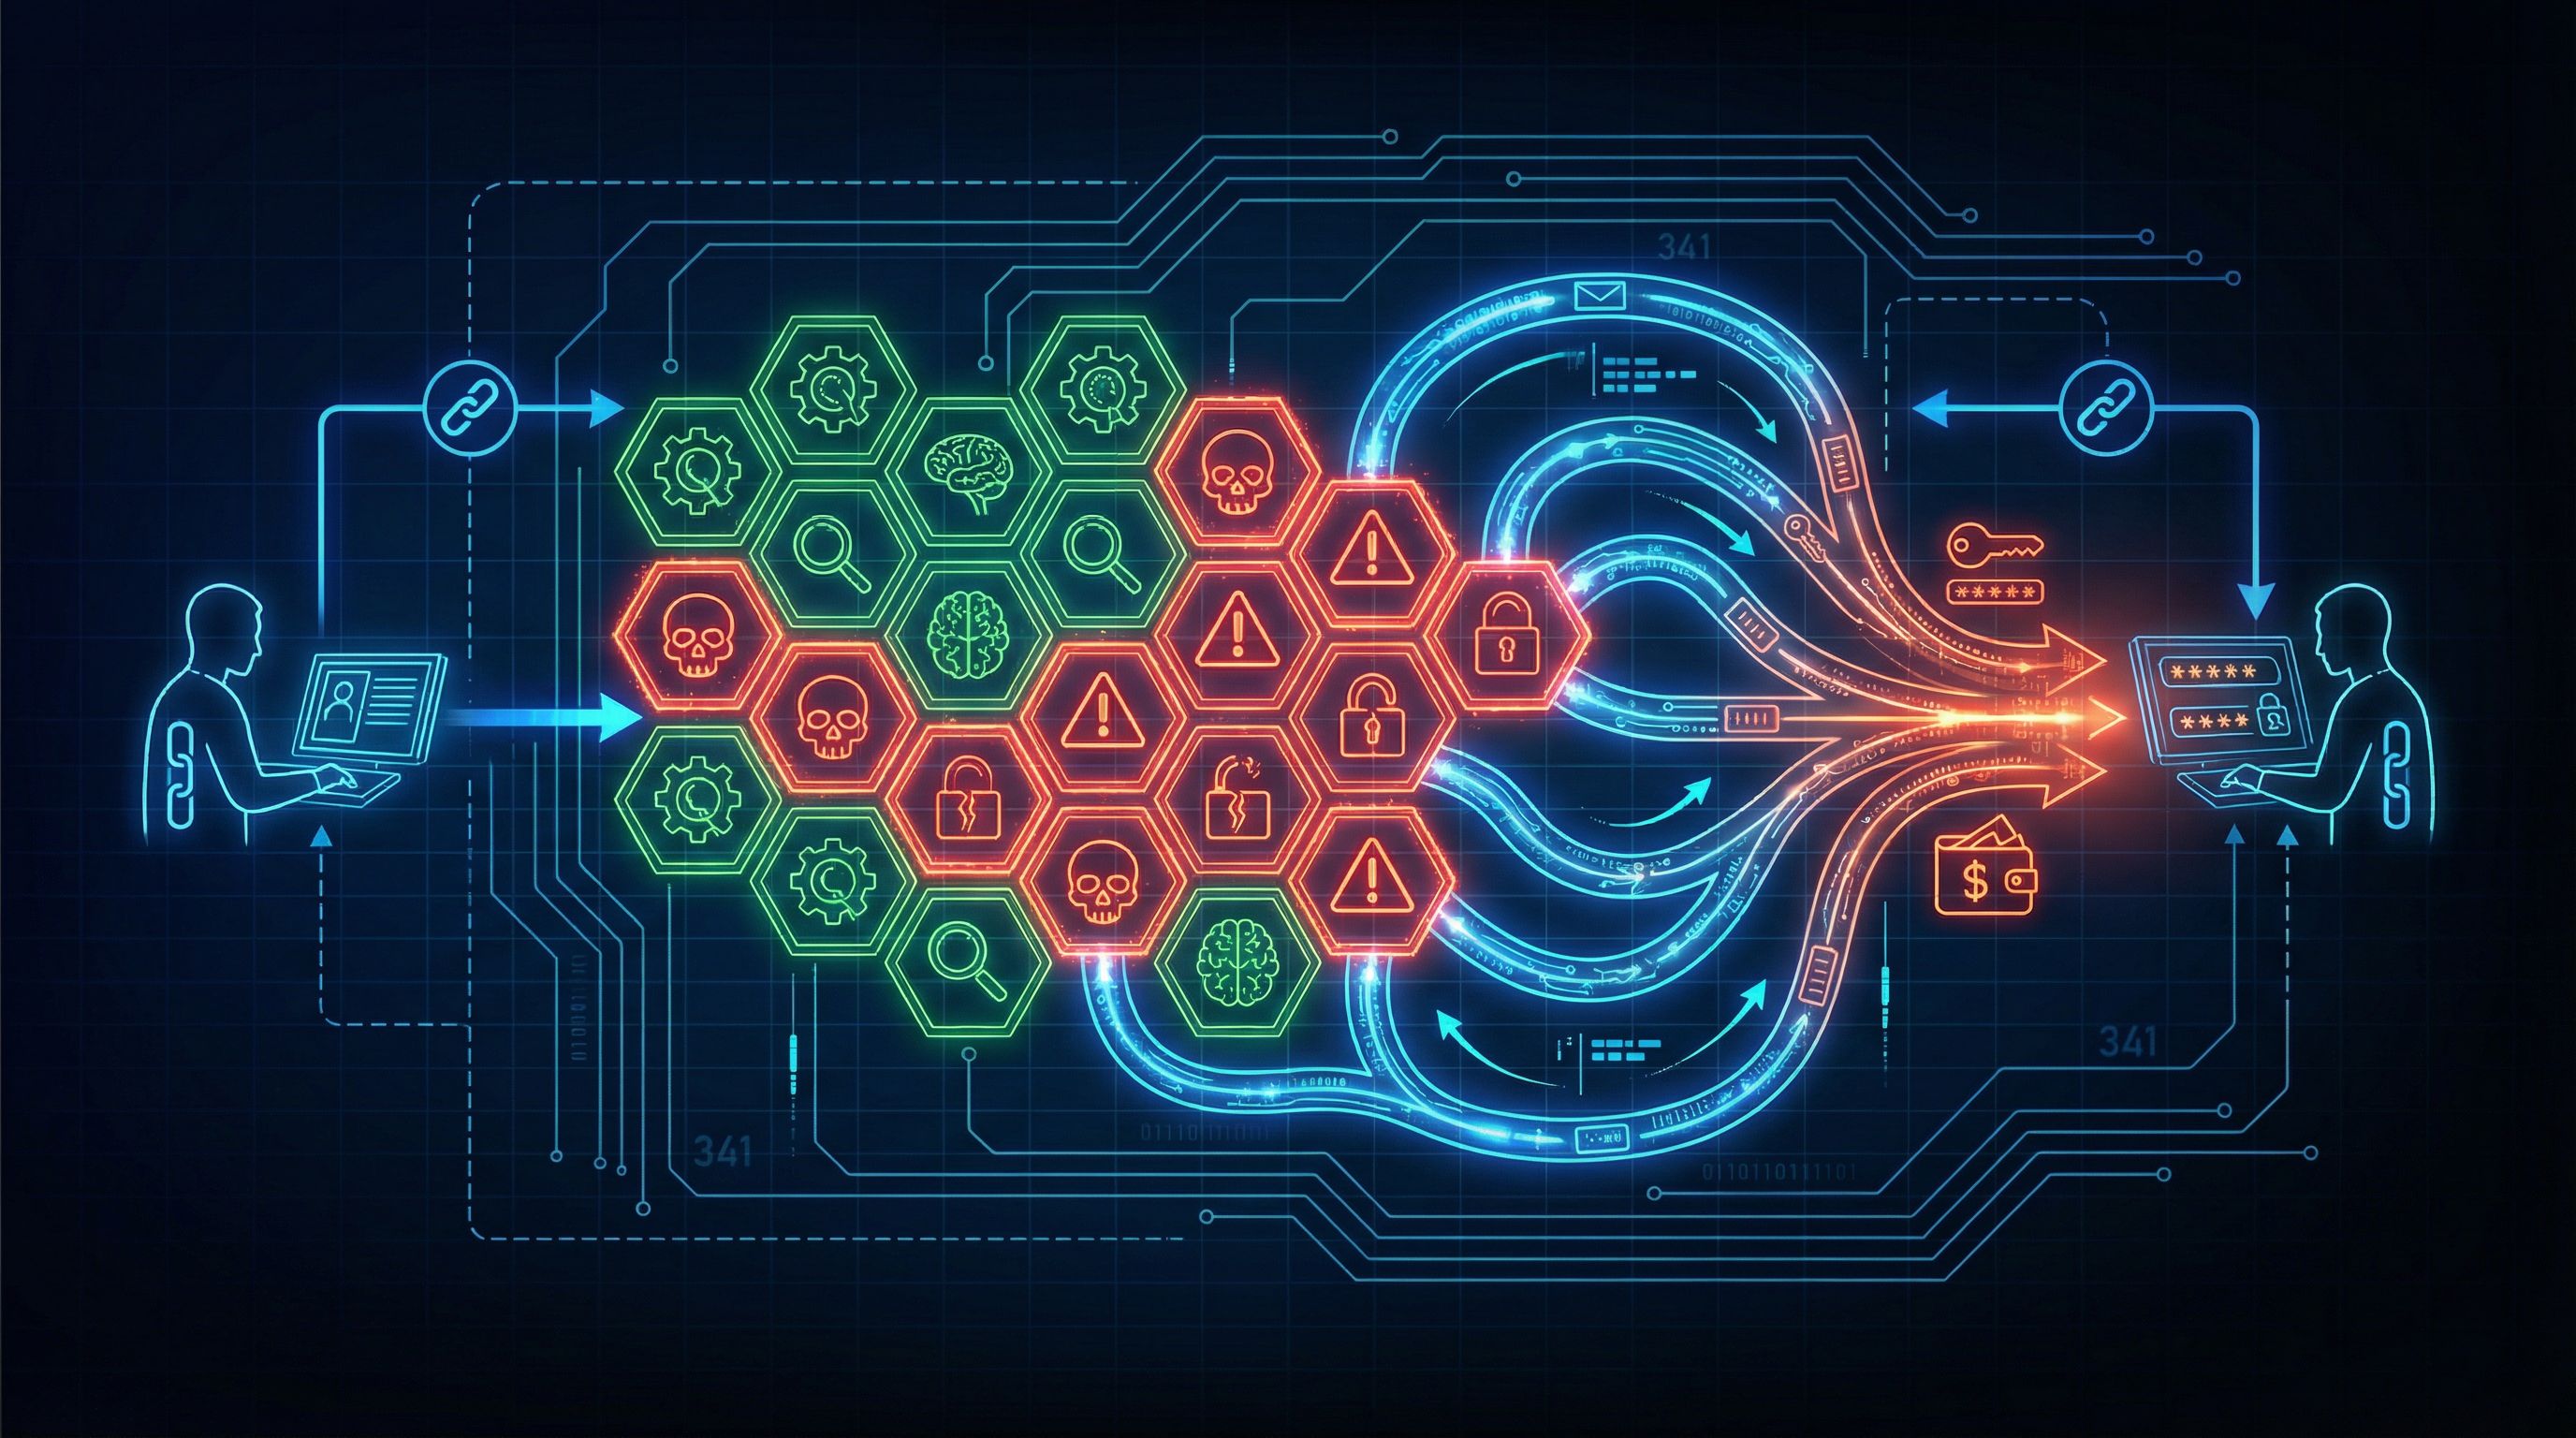
The attack chain worked like this. You install what looks like a legitimate skill, maybe solana-wallet-tracker or youtube-summarize-pro. The skill's documentation mentions a "Prerequisites" section requiring you to install something first. On Windows, users were directed to download a password-protected ZIP archive from a GitHub repository containing an executable named openclaw-agent.exe. Multiple antivirus engines identified it as a packed trojan designed to steal sensitive information.
macOS users received a different payload. The installation script, hosted on a code-sharing platform, contained obfuscated shell commands. These fetched and executed Atomic Stealer (AMOS), a commodity infostealer available for $500 to $1,000 per month on underground markets. Atomic Stealer is particularly effective at harvesting browser credentials, passwords, and cryptocurrency wallet private keys.
The compromised systems exposed everything an attacker could want: API keys, cryptocurrency exchange credentials, bot environment variables stored in the standard .clawdbot/.env file, SSH credentials, browser passwords, and wallet private keys. Some skills embedded reverse shell backdoors within otherwise functional code, giving attackers persistent access. Others exfiltrated data to webhook endpoints, making detection harder because the traffic looked like normal API calls.
All 335 skills in the primary campaign shared identical command-and-control infrastructure, suggesting a single threat actor behind most of the operation. The C2 server at 91.92.242.30 coordinated the attack across both operating systems.
The Broader Ecosystem Problem
Two days after the Koi Security report, Snyk published the results of ToxicSkills, the first comprehensive security audit of the AI agent skills ecosystem. They scanned 3,984 skills from ClawHub and skills.sh as of February 5, 2026.
The findings were worse than expected.
13.4% of all skills (534 of 3,984) contain critical-level security issues. 36.82% (1,467 skills) have at least one security flaw of any severity. Snyk's human reviewers confirmed 76 malicious payloads across the ecosystem, with 8 malicious skills still publicly available on ClawHub at the time of publication.
The breakdown by vulnerability category is instructive. 91% of malicious skills contained prompt injection vulnerabilities compared to 0% in the legitimate top-100 most downloaded skills. 100% of confirmed malicious samples exhibited malicious code patterns. 100% of malicious skills triggered suspicious download behaviors versus 0% for legitimate skills. Secret exposure affected 10.9% of ClawHub overall and 32% of malicious samples. Third-party content risks appeared in 17.7% of all skills and 54% of malicious ones.
The attack techniques observed included external malware distribution via password-protected ZIP files with obfuscated commands, data exfiltration using base64-encoded credential theft piped to attacker infrastructure, and security disablement through jailbreak attempts and persistent backdoor installation.
Snyk identified four primary threat actors: accounts named zaycv, Aslaep123, pepe276, and moonshine-100rze. These accounts published the majority of the malicious skills across both platforms.
Why ClawHub Was Vulnerable
The vulnerability is architectural, not incidental.
ClawHub is open by default. Anyone can upload skills. The only restriction at this stage is that a publisher must have a GitHub account at least one week old. There is no code review, no security scanning, no sandboxing, and no verification that the skill does what it claims.
This design choice made sense when the ecosystem was small and the threat model was theoretical. It stopped making sense the moment agent skills became valuable targets.
The problem compounds because of how agent skills work. Unlike browser extensions or npm packages, which operate in relatively sandboxed environments, AI agent skills run with significant local access. They can read files, execute commands, make network requests, and interact with sensitive credentials stored in environment variables. The agent trusts the skill implicitly because the skill is, by design, supposed to extend the agent's capabilities.
Peter Steinberger, OpenClaw's creator, implemented a community reporting system in response to the disclosure. Signed-in users can now flag suspicious skills. Skills receiving more than three unique reports are auto-hidden by default. This is a reasonable short-term mitigation, but it relies on the community identifying malicious skills after they have been distributed rather than preventing their publication in the first place.
The Lethal Trifecta
Simon Willison, one of the most respected voices in the Python and AI communities, articulated the fundamental problem last year: any system that combines access to private data, exposure to untrusted content, and the ability to communicate externally is vulnerable to instruction injection through any untrusted input channel.
He calls this the "lethal trifecta." Most agent skill installations have all three conditions.
Access to private data? Agent skills routinely access environment variables containing API keys, read local files, and interact with databases. Exposure to untrusted content? The skill itself is untrusted content. You downloaded it from a marketplace with no security review. Ability to communicate externally? Skills can make HTTP requests, which is how they exfiltrate stolen credentials.
The ClawHavoc attack did not exploit a bug in OpenClaw. It exploited the fundamental architecture of trusting arbitrary code downloaded from the internet to run with privileged access.
What This Means for Enterprise AI Deployments
If you are building production AI systems, the ClawHub attack should inform your security posture in several concrete ways.
First, treat agent marketplaces like untrusted code sources. The convenience of "just install a skill" comes with the same risks as downloading random executables from the internet. Before installing any community skill, review the source code. Check the publisher's history. Verify that the skill's permissions match its stated functionality. A YouTube summarization tool should not need access to your cryptocurrency wallet or SSH credentials.
Second, implement least-privilege architectures. Your AI agent should not run with access to everything on the machine. Containerize agent workloads. Restrict network access to only the endpoints the agent legitimately needs. Store sensitive credentials in a secrets manager with scoped access rather than in flat environment files.
Third, audit installed skills regularly. Snyk released uvx mcp-scan@latest --skills as a command-line tool for auditing installed skills against known malicious packages. Run this on any machine where agents operate. If you installed skills from the known threat actors (zaycv, Aslaep123, pepe276, moonshine-100rze), rotate every credential that skill could have accessed.
Fourth, monitor for anomalous behavior. Skills that suddenly start making requests to unusual endpoints, accessing files outside their normal scope, or executing shell commands they should not need are exhibiting indicators of compromise. Runtime monitoring tools like Agent Guard can detect these patterns.
Fifth, prefer building over downloading for sensitive integrations. For anything that touches production data, customer information, or financial systems, build your own integrations rather than trusting community skills. The development cost is measurable. The cost of a data breach is not.
The Parallels to Previous Ecosystem Attacks
The AI agent skills ecosystem is repeating patterns we have seen before.
In 2016, a developer unpublished a tiny npm package called left-pad. Thousands of projects broke because they depended on it. The incident exposed how fragile supply chains become when everyone depends on code they have not reviewed.
In 2022, a developer intentionally sabotaged two of his popular npm packages, colors and faker, in protest of open-source economics. Thousands of applications started printing garbage to consoles.
In 2024, the xz-utils backdoor revealed a years-long social engineering campaign where an attacker patiently gained maintainer trust in a critical compression library, then inserted a sophisticated backdoor that would have affected virtually every Linux distribution.
The ClawHub attack is simpler than xz-utils but follows the same playbook: find a trusted distribution channel, publish malicious code that looks legitimate, and wait for users to install it. The difference is that AI agent skills are younger, less scrutinized, and designed to run with more privileges than most packages.
The npm and Python ecosystems spent years building security infrastructure: vulnerability databases, automated scanning, two-factor authentication requirements for package maintainers, code signing, and reproducible builds. The AI skills ecosystem has none of this infrastructure yet. ClawHavoc is the event that forces the community to start building it.
The Path Forward
The organizations leading AI agent development are responding. OpenClaw is implementing community reporting and exploring automated scanning. Snyk has released scanning tools specifically for MCP and agent skills. The Model Context Protocol specification now includes security annotations that allow tools to declare their required permissions.
But the fundamental tension remains: agent skills are useful precisely because they can do things. Reading files, making API calls, executing code. The same capabilities that make skills powerful make them dangerous when malicious.
The likely evolution follows the mobile app store model. Expect to see tiered trust levels where verified publishers who undergo identity verification and code review receive preferential treatment. Expect runtime permission prompts where skills must request specific capabilities and users must approve them. Expect sandboxed execution where skills run in isolated environments with explicit API bridges to the host system. Expect audit logging where every action a skill takes is logged and reviewable.
This infrastructure will take years to mature. In the meantime, treat every community-distributed AI skill as potentially hostile code.
The Vindler Perspective
At Vindler, we have been saying for a year that the convenience of AI-generated and AI-downloaded code comes with hidden costs. That is why our senior engineers understand every dependency they ship.
Vibe coding is letting an LLM install packages you have not reviewed. Vibe coding is trusting marketplace ratings over source code audits. Vibe coding is building systems where no one understands what runs in production.
The 341 malicious ClawHub skills were installed by people who vibed. They saw a skill that claimed to do something useful, clicked install, and never read a line of code. Some of those people lost cryptocurrency. Some lost API keys. Some have backdoors on their machines that have not been discovered yet.
We build AI systems differently. Every integration is code we wrote or code we reviewed. Every dependency is evaluated for security posture. Every production system runs with least-privilege access. When we build MCP servers or agent skills for clients, we deliver source code with documentation, not just a marketplace link.
The ClawHub attack validates what production engineering has always known: convenience has a price, and you pay it when something goes wrong.
If you are building AI agents for enterprise use and want the confidence that comes from understanding every line of code in your system, that is what we do.
The Vindler team builds secure, audited AI integrations for enterprises, from OpenClaw skills to MCP servers. If you are deploying AI agents and want engineers who understand the security landscape from hands-on experience, reach out.